What is Penetration Testing?
Penetration testing, or pentesting, is an authorized simulated cyberattack used to identify and exploit security weaknesses in systems, networks, applications, APIs, and other technology. A penetration tester uses many of the same techniques as a real attacker to determine not only whether vulnerabilities exist, but whether they can actually be exploited and what an attacker could achieve.
Unlike automated vulnerability scanning, penetration testing involves human analysis and hands-on exploitation. A typical penetration test includes reconnaissance, vulnerability discovery, exploitation, privilege escalation, validation of attack paths, and reporting so organizations can prioritize remediation based on real-world risk.
Types of Penetration Testing
Penetration tests can be categorized by how much information and access the tester receives and by the systems or environments being tested. The right approach depends on the organization’s goals, scope, and the types of threats it wants to evaluate.
Penetration Testing Approaches
Black Box Testing
In a black box penetration test, the tester has little to no prior knowledge of the target environment. This approach more closely simulates an external attacker who must first gather information about the target before attempting to identify and exploit vulnerabilities.
Gray Box Testing
In a gray box penetration test, the tester receives limited information or access, such as user credentials or basic details about the environment. This can simulate an attacker who has gained some level of access or an authorized user attempting to move beyond their permissions.
White Box Testing
In a white box penetration test, the tester has extensive knowledge of the target environment, which may include architecture details, credentials, source code, or other internal information. This allows for a more comprehensive assessment of potential security weaknesses.
Penetration Testing By Target
Network Penetration Testing
Tests network infrastructure to identify exploitable weaknesses such as misconfigurations, exposed services, insecure protocols, and other vulnerabilities that could enable unauthorized access.
Web Application Penetration Testing
Tests web applications for exploitable vulnerabilities such as SQL injection, cross-site scripting, authentication weaknesses, access control issues, and insecure application configurations.
API Penetration Testing
Tests APIs for vulnerabilities involving authentication, authorization, data exposure, input validation, business logic, and other weaknesses attackers could exploit.
Cloud Penetration Testing
Evaluates cloud environments for vulnerabilities and misconfigurations involving identities and permissions, storage, workloads, services, and other cloud resources.
Wireless Penetration Testing
Tests wireless networks and devices for weaknesses such as insecure encryption, authentication vulnerabilities, rogue access points, and configurations that could expose network traffic or provide unauthorized access.
Mobile Application Penetration Testing
Tests mobile applications for weaknesses involving authentication, data storage, network communications, APIs, platform-specific controls, and other vulnerabilities that could expose sensitive information or functionality.
Internal vs. External Penetration Testing
Internal Penetration Testing
Evaluates what an attacker could access or accomplish from inside the network, such as after compromising an employee account or device.
External Penetration Testing
Assesses internet-facing systems and services from outside an organization’s network, simulating threats from an external attacker.
Penetration Testing Process
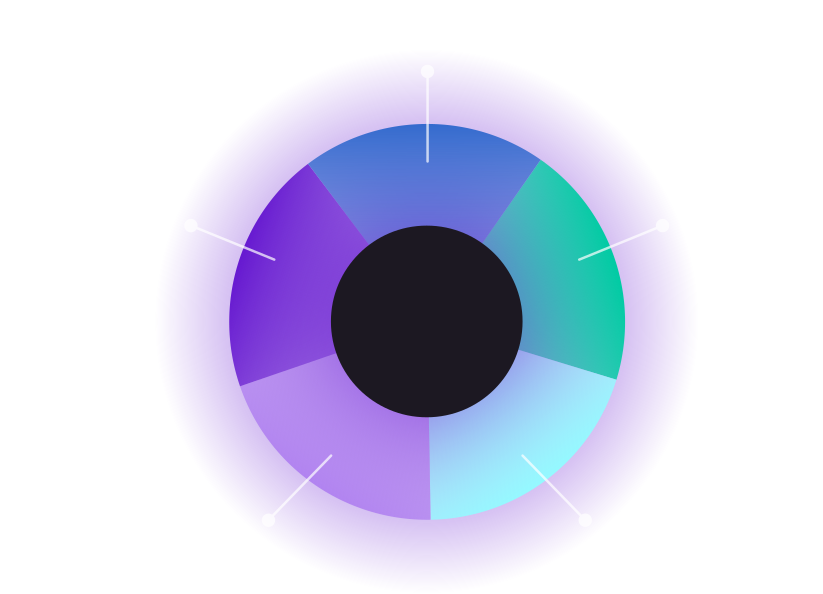
Before testing begins, the organization and penetration tester define the scope, objectives, authorized targets, and rules of engagement for the assessment. Once these parameters are established, penetration testing usually involves the following five steps:
-
01
Reconnaissance
The initial stage of penetration testing, known as reconnaissance, forms the foundation of the entire process. During this phase, the pen tester undertakes an intelligence-gathering mission to gather information about the target system. This includes details like IP addresses, domain information, network services, mail servers, and network topology.
-
02
Scanning
During this phase, a thorough technical examination of the target system takes place. Tools such as port scanners, vulnerability scanning software and network mappers are employed to gain information about the target systems.
Scanning allows testers to assess the behavior of the target application in different scenarios and pinpoint potential vulnerabilities that could be exploited.
-
03
Exploitation and Vulnerability Verification
In this phase, the penetration testers may attempt to exploit the vulnerable areas located within the scope of the penetration test. This phase also allows the penetration tester and the organization to verify the severity of weaknesses identified within the systems.
-
04
Maintaining Access and Privilege Escalation
Once the pen testers have access to the target environment, they maintain access and escalate privileges, attempting to move laterally through the system and access sensitive data and systems.
-
05
Reporting and Documentation
At the final stage, the penetration testers compile their observations, findings, and remediation steps into a report for the target organization. The report includes pertinent recommendations for the organization to enhance its security measures.
What Happens After a Penetration Test?
After identified vulnerabilities are remediated, organizations may conduct retesting to verify that the weaknesses have been resolved and that the fixes haven’t introduced additional security issues.
Penetration Testing vs. Red Teaming
Both red teaming and penetration testing involve using ethical hackers to identify security vulnerabilities, but they differ in terms of scope, objectives, approach, and depth. Here are some of the differences between red teaming and penetration testing:
Scope and Approach
Penetration Testing
Typically focuses on identifying vulnerabilities in a specific system, application, or network. It follows a systematic approach aiming to uncover vulnerabilities and provide recommendations for remediation.
Red Teaming
Takes a broader and more holistic approach by simulating real-world attacks. It involves an organized team working to simulate a simulated attack campaign with predefined objectives, which may involve multiple systems, applications, and even physical security measures.
Objectives
Penetration Testing
Assess security weaknesses by finding and exploiting as many vulnerabilities as possible. The focus is on uncovering technical vulnerabilities and providing recommendations for improving security.
Red Teaming
Aims to simulate realistic and targeted attacks to identify weaknesses in an organization’s overall security posture. It assesses people, processes, and technologies to provide a more comprehensive evaluation of an organization’s ability to detect and respond to advanced threats.
Approach to Testing
Penetration Testing
Typically follows a predefined methodology, involving specific tools and techniques to uncover vulnerabilities and assess their impact.
Red Teaming
Takes a more adversarial approach by aiming to replicate an attacker’s perspective. It involves creative thinking, reconnaissance, and social engineering techniques to bypass defenses and simulate real-world attack scenarios.
Engagement Duration and Depth
Penetration Testing
Engagements tend to be shorter in duration and focused on a specific target. The testing is often conducted within a predefined time frame, with a set of specific objectives.
Red Teaming
Engagements are typically longer in duration and involve a more comprehensive assessment of an organization’s security.
Penetration Testing vs. Vulnerability Scanning
Penetration testing and vulnerability scanning both help identify security weaknesses, but they serve different purposes. Vulnerability scanning typically uses automated tools to identify known vulnerabilities and potential security issues. Penetration testing goes further by using hands-on techniques to validate vulnerabilities, attempt exploitation, and determine the potential impact of an attack.
Approach
Penetration Testing: Human-led, supported by tools
Vulnerability Scanning: Primarily automated
Goal
Penetration Testing: Validate and exploit security weaknesses
Vulnerability Scanning: Identify potential vulnerabilities
Exploitation
Penetration Testing: Yes, within an authorized scope
Vulnerability Scanning: Typically no
Attack Paths
Penetration Testing: Can combine weaknesses to demonstrate attack paths
Vulnerability Scanning: Identifies individual findings
Results
Penetration Testing: Validated findings, potential impact, and remediation guidance
Vulnerability Scanning: List of detected vulnerabilities
Frequency
Penetration Testing: Typically performed periodically or after significant changes
Vulnerability Scanning: Often performed regularly or continuously
Vulnerability scanning and penetration testing are complementary security practices. Regular scanning can identify potential weaknesses at scale, while penetration testing provides deeper validation of whether those weaknesses can be exploited and what an attacker could achieve.
Penetration Testing Tools
Penetration testers use a variety of tools to discover, analyze, and validate vulnerabilities across networks, applications, and systems. The tools used depend on the scope and objectives of the penetration test. Common penetration testing tools include Kali Linux, Burp Suite, Wireshark, John the Ripper, Hashcat, and Nmap.
Kali Linux
Open Source
Penetration Testing Platform
Kali Linux is an open-source, Debian-based Linux distribution designed for penetration testing, security research, computer forensics, reverse engineering, and other information security tasks. Developed and maintained by OffSec, Kali Linux includes hundreds of tools that support different stages of penetration testing, from reconnaissance and vulnerability analysis to exploitation and post-exploitation.
Burp Suite
Free + Paid
Web Application Security Testing
Burp Suite is a web application security testing platform developed by PortSwigger. Penetration testers use Burp Suite to intercept, inspect, and modify HTTP and HTTPS traffic between a browser and web application.
Its tools can help testers identify and validate web application vulnerabilities involving authentication, access controls, session management, input validation, and other application security weaknesses.
Wireshark
Open Source
Network Traffic Analysis
Wireshark is an open-source network protocol analyzer used to capture and inspect network traffic. Penetration testers can use Wireshark to analyze packets and protocols, investigate suspicious network behavior, identify insecure communications, and uncover configuration or implementation issues that could create security risks.
Wireshark supports hundreds of network protocols and provides filtering and analysis capabilities that help testers understand how systems communicate across a network.
John the Ripper
Open Source
Password Security Auditing
John the Ripper is an open-source password security auditing and recovery tool. Penetration testers can use it to test password strength by attempting to recover passwords from captured or obtained password hashes using techniques such as dictionary and brute-force attacks.
It supports numerous hash and cipher types and can help testers identify weak passwords that could provide an attacker with unauthorized access.
Hashcat
Open Source
Password Recovery and Auditing
Kali Linux is an open-source, Debian-based Linux distribution designed for penetration testing, security research, computer forensics, reverse engineering, and other information security tasks. Developed and maintained by OffSec, Kali Linux includes hundreds of tools that support different stages of penetration testing, from reconnaissance and vulnerability analysis to exploitation and post-exploitation.
Kali Linux is an open-source, Debian-based Linux distribution designed for penetration testing, security research, computer forensics, reverse engineering, and other information security tasks. Developed and maintained by OffSec, Kali Linux includes hundreds of tools that support different stages of penetration testing, from reconnaissance and vulnerability analysis to exploitation and post-exploitation.
Nmap
Open Source
Network Discovery and Scanning
Nmap (Network Mapper) is an open-source tool for network discovery and security auditing. Penetration testers commonly use Nmap during reconnaissance and scanning to identify hosts, open ports, running services, operating systems, and other information about a target environment.
This information helps testers understand a network’s attack surface and identify systems and services that may require further investigation.
What Are the Goals of Penetration Testing?
-
01
Identify Security Weaknesses
Penetration testing helps identify and validate vulnerabilities in an organization’s systems, networks, and applications so security teams can address weaknesses before they can be exploited by attackers.
-
02
Validate Security Controls
Penetration testing helps organizations evaluate whether existing security controls can prevent or limit real-world attacks. By attempting to bypass these controls within an authorized scope, testers can identify gaps that may leave systems or data exposed.
-
03
Assess Potential Impact
Penetration testing goes beyond identifying vulnerabilities by demonstrating how weaknesses could be exploited and what an attacker could potentially access or accomplish. This helps organizations better understand the real-world risk associated with security vulnerabilities.
-
04
Compliance and Regulations
Penetration testing can help organizations meet security testing requirements associated with regulatory and industry standards. It can also provide evidence that security controls and vulnerabilities are being regularly assessed and addressed.
Why Penetration Testing Training Matters
Penetration testing training is critical for pentesting teams as it enhances their technical skills and knowledge, keeps them updated with evolving threats, establishes effective testing methodologies, ensures compliance with regulations, and improves communication and reporting capabilities. By investing in training, organizations can build highly skilled pentesting teams that can effectively evaluate and strengthen their security posture.
Benefits of Penetration Testing
-
Understand Real-World Risk
Penetration testing goes beyond identifying potential vulnerabilities by demonstrating how weaknesses could be exploited and what impact a successful attack could have.
-
Prioritize Remediation
Validated findings help security teams focus remediation efforts on vulnerabilities and attack paths that present meaningful risk rather than treating every finding equally.
-
Identify Gaps Between Security Controls
Individual security controls may work as intended while combinations of weaknesses still create exploitable attack paths. Penetration testing can uncover these gaps by evaluating systems from an attacker’s perspective.
-
Improve Security Investments
Findings from penetration tests can help organizations understand where additional controls, configuration changes, training, or other security investments may be needed.
How to Learn Penetration Testing
Penetration testing requires hands-on experience with the tools, techniques, and methodologies used to identify and exploit security weaknesses. OffSec's penetration testing training provides a progression from foundational skills to advanced techniques, allowing learners to build practical skills through hands-on labs and real-world scenarios.
Build Foundational Penetration Testing Skills

Network Penetration Testing Essentials
This is a fundamental-level Learning Path designed to prepare learners to begin their penetration testing journey. This learning path covers the main concepts of information security such as cryptography, scripting, networking protocols, and working with shells.
Develop Practical Penetration Testing Skills

PEN-200: Penetration Testing with Kali Linux
The PEN-200 course with OffSec Certified Professional (OSCP) certification provides practical, real-world training that equips teams with the skills and knowledge needed to conduct thorough and effective assessments.
Expand into Specialized Penetration Testing

PEN-210: Wireless Network Attacks
Develop skills for assessing and securing wireless networks, including identifying and exploiting vulnerabilities in wireless environments.
Advance Your Penetration Testing Skills

PEN-300: Evasion Techniques and Breaching Defenses
PEN-300 builds advanced penetration testing skills for attacking mature environments, including techniques for bypassing security defenses and identifying complex attack paths.
Start Your Penetration Testing Training
Build hands-on penetration testing skills with OffSec training for individuals and teams.
Best value
Learn One
$2,749/year*
Includes one year of access to one 200 or 300-level course, the associated labs, and two exam attempts
Large teams
Learn Enterprise
Custom pricing
Unlimited OffSec Learning Library access with flexible terms and volume discounts available