What Are Wireless Network Attacks?
Wireless networks such as Wi-Fi, mobile networks, and Bluetooth are widely used to connect devices and access data. While they provide flexibility and convenience, they can also introduce cybersecurity risks.
Wireless network attacks are attempts to exploit weaknesses in wireless communication systems. Attackers may use these vulnerabilities to intercept data, gain unauthorized access, disrupt networks, or compromise connected devices. Because wireless networks transmit data over the air, they can provide additional opportunities for attackers compared with wired networks.
Strong wireless security controls, encryption, authentication, and regular security testing help protect wireless networks from attacks and reduce the risk of unauthorized access, data loss, and network disruption.
What is Wireless Networking?
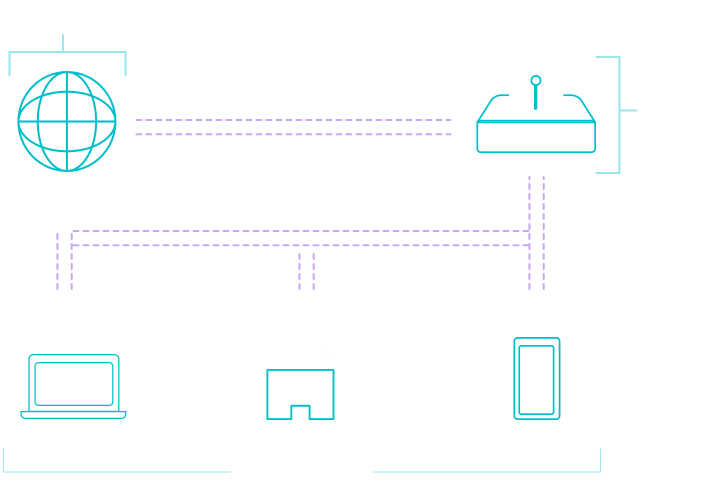
Wireless networking is a technology that allows devices to connect and communicate without the need for physical wires or cables. This kind of connectivity is facilitated by emitting and receiving electromagnetic waves, usually radio frequencies (RF).
How Wireless Networks Operate
Transmitter and Receiver
At its core, wireless communication involves a transmitter and a receiver. The transmitter sends out data in the form of electromagnetic waves, while the receiver captures these waves and decodes them back into usable data.
Access Points
In a typical wireless network, such as a Wi-Fi setup, an access point (often integrated into a router) serves as the central hub. Devices connect to this hub to access the network. The access point manages traffic and ensures data reaches the correct device.
Frequency Bands
Wireless networks operate on specific frequency bands. Commonly used bands include 2.4 GHz and 5 GHz for Wi-Fi. The chosen frequency affects the range and speed of the network.
Modulation
This is the process of converting digital data into radio waves. Different wireless standards use various modulation techniques to optimize data transfer rates and reliability.
Popular Wireless Networking Standards
Wi-Fi (IEEE 802.11 standards)
- 802.11a: Operates in the 5 GHz band and offers speeds up to 54 Mbps.
- 802.11b: Works in the 2.4 GHz band with speeds up to 11 Mbps.
- 802.11g: Uses the 2.4 GHz band, offering improvements over 802.11b with speeds up to 54 Mbps.
- 802.11n: Supports both 2.4 GHz and 5 GHz bands. Introduced Multiple Input Multiple Output (MIMO) technology, allowing for increased throughput with speeds potentially reaching 600 Mbps.
- 802.11ac: Operates primarily in the 5 GHz band. Enhanced MIMO technology and wider channel bandwidth lead to potential speeds over 1 Gbps.
- 802.11ax (Wi-Fi 6): A more recent standard, Wi-Fi 6 offers better performance in crowded areas, improved latency, and potential speeds up to 10 Gbps.
Bluetooth
A short-range wireless communication technology designed for transferring data between devices in close proximity. Over the years, Bluetooth has seen various versions, each improving on speed, range, and security.
Zigbee
A low-power, low-data rate wireless communication protocol often used in home automation and Internet of Things (IoT) devices. It is designed to be efficient, with a focus on low power consumption and deep penetration in challenging environments.
Common Types of Wireless Network Attacks
Wireless networking is a technology that allows devices to connect and communicate without the need for physical wires or cables. This kind of connectivity is facilitated by emitting and receiving electromagnetic waves, usually radio frequencies (RF).
Eavesdropping
Eavesdropping, or sniffing, is a passive attack where an attacker intercepts wireless network traffic. The attacker monitors communications between devices and wireless access points to capture sensitive information.
How does it work?
Capturing airborne Data
Since wireless networks operate by transmitting data using electromagnetic waves, these signals can be captured by any device within range that’s equipped with the appropriate receiving antenna and software.
Decoding
If the data is unencrypted, an eavesdropper can easily read the captured data directly. However, if the data is encrypted, the attacker would need additional tools or techniques to decode and understand the intercepted information.
Sniffing Tools
There are software tools specifically designed to facilitate sniffing, allowing attackers to analyze and sort the captured data packets. Examples include Wireshark and Aircrack-ng.
Man-In-The-Middle Attacks (MITM)
A Man-in-the-Middle (MITM) attack occurs when an attacker intercepts and relays communication between two parties. This allows the attacker to monitor or potentially modify data while making both parties believe they are communicating directly.
How does it work?
Interception
The attacker first needs to insert themselves between the victim and the entity they are communicating with (e.g., between a user and a Wi-Fi network).
Decryption
If the intercepted data is encrypted, the attacker would need to decrypt it. This can be done using various techniques, one common method being the use of rogue Wi-Fi access points in wireless network scenarios.
Relay and Capture
The attacker captures the outgoing messages from a source, potentially alters them, and then sends them to the intended recipient. The recipient, believing the communication is secure, responds, which the attacker can again capture, alter, and relay.
Termination
Once the attacker has gained the desired information or caused sufficient disruption, they can end the session, and the victims might remain unaware of the breach.
Evil Twin Attack
An Evil Twin attack uses a rogue wireless access point that impersonates a legitimate Wi-Fi network. Users who connect to the fake network may unknowingly expose credentials, data, or other sensitive information to the attacker.
How does it work?
Setup
The attacker configures a device to act as a wireless access point, often using a common network name (SSID) that potential victims might recognize, such as “Free Airport Wi-Fi” or duplicating the name of a nearby legitimate network.
Broadcasting
The evil twin access point broadcasts its SSID, waiting for devices to connect to it. In some scenarios, an attacker might also deploy a jamming attack on the legitimate access point to make users more likely to connect to the stronger-signal evil twin.
Interception
Once a user connects to the evil twin, they may be presented with a fake login page to capture credentials, or the attacker can simply monitor their online activity, capturing any unencrypted data that is transmitted.
Manipulation
In advanced scenarios, the attacker might alter the data being sent or received by the victim or redirect them to malicious websites.
WEP/WPA Key Cracking
WEP/WPA key cracking attempts to obtain wireless encryption keys without authorization. Attackers can use compromised keys to gain network access and potentially intercept or modify traffic. WEP is outdated and insecure, while modern wireless networks should use stronger protocols such as WPA3.
Common tools:
Aircrack-ng
Perhaps the most popular suite of tools for cracking wireless encryption. It can crack WEP keys and retrieve the passphrase from WPA/WPA2-protected networks given enough data packets.
Airsnort
Another tool for decrypting WEP encryption on Wi-Fi networks. It passively monitors transmissions and computes encryption keys once it gathers enough packets.
Wireshark
A network protocol analyzer, not exclusively for wireless cracking but can be used in tandem with other tools to capture packets and analyze traffic.
Reaver
This tool specifically targets WPS (Wi-Fi Protected Setup) vulnerabilities in routers, which can indirectly compromise WPA/WPA2 security.
Kismet
A wireless network detector, sniffer, and intrusion detection system. It can be used to detect networks and capture data packets, which can later be used to crack encryption keys.
Deauthentication Attacks
A deauthentication attack sends forged Wi-Fi deauthentication frames to disconnect devices from an access point. This can disrupt wireless connectivity and may be used as part of other wireless attacks.
How do deauthentication attacks work?
Frame spoofing
The attacker sends fraudulent deauthentication frames (packets) to either the client or the access point. These frames are crafted to appear as if they come from the other party.
Disconnection
Upon receiving these frames, the targeted device (either the client or the access point) terminates the connection, believing it to be a legitimate request.
Network disruption
The attack can be continuous, sending deauthentication frames at intervals to keep the device disconnected or prevent reconnection, causing persistent disruptions.
Defense and Mitigation Strategies for Wireless Network Attacks
-
Regularly Update and Patch Firmware
Manufacturers often release firmware updates to patch known vulnerabilities. Regularly check the manufacturer’s website or set up alerts for updates. Set a routine (e.g., monthly or quarterly) to verify that all network devices are running the latest firmware versions.
-
Use Strong Encryption Methods
WPA3 is the latest and most secure encryption standard for Wi-Fi networks. Upgrade devices to support and use WPA3. If WPA3 isn’t an option, make sure to use at least WPA2 and avoid using outdated encryption methods like WEP.
-
Implement MAC Address Filtering
By allowing only specific MAC addresses (hardware IDs of devices), you can ensure that only authorized devices can connect to the network. Periodically review and update the list of allowed MAC addresses, removing any that are no longer in use or necessary.
-
Turn Off SSID Broadcasting
Disabling SSID broadcasting makes your network invisible to casual scans, reducing the likelihood of opportunistic attacks.
-
Use VPNs on Public Networks
VPNs (Virtual Private Networks) create an encrypted tunnel for your data. Even if someone intercepts it, they won’t be able to read its contents. This is crucial on public networks. Users should always connect via a VPN to shield your online activities from prying eyes.
-
Perform Regular Security Audits and Penetration Testing
Performing regular audits will help identify any weaknesses in your network’s defenses. Penetration testing, where ethical hackers attempt to breach your defenses, can provide insights into potential vulnerabilities and areas for improvement.
Dangers of Wireless Network Attacks
-
Unauthorized Access to Sensitive Data
A compromised wireless network can expose personal and business data, including emails, documents, financial records, credentials, and intellectual property. Attackers may use stolen credentials to access accounts, commit fraud, or cause further damage.
-
Potential for Malware Installation
Attackers who gain network access may install malware, backdoors, or spyware. These threats can provide persistent access, monitor user activity, capture keystrokes, and steal sensitive data.
-
Misuse of Network Resources
Attackers can use compromised networks and devices for malicious activity. Infected devices may become part of botnets used in Distributed Denial of Service (DDoS) attacks. Unauthorized activity can also consume network bandwidth and disrupt legitimate users.
-
Threat to Smart Devices and IoT
Weakly secured Internet of Things (IoT) devices, such as cameras and smart home systems, can be compromised through an attacked wireless network. Attackers may use these devices to monitor users, disrupt connected systems, or gain access to other networks and devices.
Specialized Penetration Testing Training
OffSec is a globally recognized and trusted provider of industry-leading training and certification for network security and wireless penetration testing. Organizations worldwide turn to OffSec to enhance the skills and capabilities of security teams in the following ways:
Expand into Specialized Penetration Testing
PEN-210: Wireless Network Attacks
Develop skills for assessing and securing wireless networks, including identifying and exploiting vulnerabilities in wireless environments.
Start Your Specialized Penetration Testing Training
Develop specialized penetration testing skills with OffSec training for individuals and teams.
Best value
Learn One
$2,749/year*
Includes one year of access to one 200 or 300-level course, the associated labs, and two exam attempts
Large teams
Learn Enterprise
Custom pricing
Unlimited OffSec Learning Library access with flexible terms and volume discounts available