What is Secure Software Development?
Secure software development is a comprehensive approach to building software applications with a strong focus on protecting sensitive data and preventing security breaches. It involves integrating security measures from the very beginning of the development process, ensuring that security considerations are woven into the fabric of the application. Secure software development encompasses a set of best practices, coding standards, and principles that address common security threats and vulnerabilities.
Penetration Testing Process
Before testing begins, the organization and penetration tester define the scope, objectives, authorized targets, and rules of engagement for the assessment. Once these parameters are established, penetration testing usually involves the following five steps:
-
01
Planning
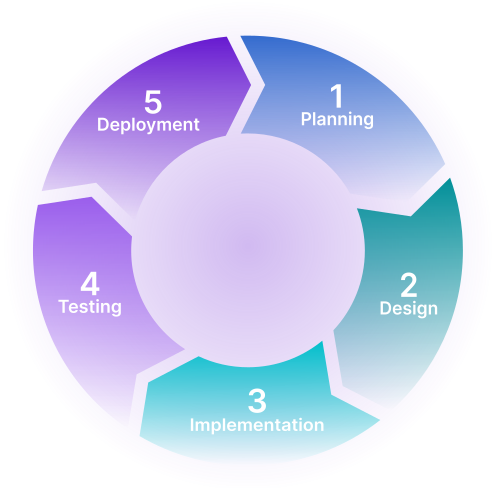
In the planning phase of the SDLC, the development team outlines the software’s scope and objectives. Security is integrated into this phase by considering security risks and establishing security requirements for the application. Security requirements can include access control mechanisms, threat modeling, authentication protocols, and encryption requirements.
-
02
Design
During the design phase, developers create a detailed architectural plan for the application. Secure coding principles, such as secure by design, are integrated into this phase to ensure that security is part of the software’s design. The design phase also includes setting up security protocols like Transport Layer Security (TLS) and network encryption.
-
03
Implementation
In the implementation phase, developers write the code and incorporate secure coding practices like input validation and proper error handling. Developers can use code analysis tools for secure coding practices and identify vulnerabilities before the code is deployed. Code reviews and testing tools can ensure that the code adheres to security standards.
-
04
Testing
In this phase, developers test the code for functionality, performance, and security. Security testing techniques focus on discovering vulnerabilities in the software application, such as penetration testing and vulnerability scanning, to identify security flaws in the application.
-
05
Deployment
During this phase, developers deploy the software application and ensure that the environment in which the application operates meets the necessary security requirements. Security is integrated into this phase by ensuring that access controls and network security mechanisms, such as firewalls, are in place.
Key Secure Software Development Principles
The three fundamental principles that guide software development maintain the confidentiality, integrity, and availability of software applications while ensuring that they remain resilient to attacks and vulnerabilities.
-
Secure by design
An essential principle that involves integrating security into the software design process from the ground up. In secure by design, security is not considered an afterthought or add-on, but an essential aspect of the design process.
-
Least privilege
A fundamental aspect of secure software development that grants users the absolute minimum level of access required to execute their tasks. Developers can ensure that the least privilege principle is adhered to by granting users access to system resources based on their functional roles and responsibilities. By limiting access, the potential impact of any security breaches or unauthorized access is minimized.
-
Defense in depth
A principle of secure software development that emphasizes a layered approach to system security. In defense in depth, security is implemented by using multiple layers of protection where if one security layer fails, there are others in place to help mitigate and control the damage. These protection layers can include firewalls, access controls, intrusion detection systems, and security monitoring systems, among others.
Secure Coding Best Practices
Secure coding practices help developers build software that is resistant to common cybersecurity threats and vulnerabilities. These practices include input validation, secure authentication, session management, secure communication, and error handling. Applying them throughout the software development lifecycle helps reduce security risks and prevent vulnerabilities.
-
Input Validation
Validate and sanitize user input to prevent malicious data from reaching an application. Check input for size, type, format, and other requirements to help prevent attacks such as injection.
-
Secure Authentication
Use strong authentication to ensure only authorized users can access applications and data. Protect passwords with secure hashing algorithms such as bcrypt and use secure session tokens or cookies to manage authenticated sessions.
-
Secure Session Management
Protect user sessions from unauthorized access and session hijacking. Use secure, randomly generated session tokens and cookies, set appropriate expiration times, and apply secure cookie settings.
-
Secure Communication
Protect data in transit from unauthorized access or modification. Use secure protocols such as TLS and trusted cryptographic libraries to encrypt communications between systems.
-
Error Handling
Use error handling that helps users without exposing sensitive system information. Avoid detailed error messages that could reveal application logic, vulnerabilities, or other information useful to attackers.
What is Secure Software Development?
Secure software development training helps developers and cybersecurity professionals build and support secure applications. Developers learn how to apply secure coding practices, identify vulnerabilities early, and reduce the risk of security breaches and exploits.
For cybersecurity professionals, understanding the software development process improves collaboration with development teams. It helps security teams provide practical guidance and integrate security throughout the software development lifecycle.
Training also builds a stronger security culture by giving development and security teams a shared understanding of cybersecurity best practices. This collaboration helps organizations develop more secure software and reduce overall security risk.
Benefits of Secure Software Development
-
Reduced Breach Risks
Secure software development can help reduce the risk of data breaches. By adhering to secure coding principles and best practices, developers can identify and address potential security vulnerabilities in the software early in the development lifecycle. This, in turn, reduces the likelihood of data breaches occurring during and after deployment.
-
Improved Customer Trust
Secure software development increases customer trust by providing reliable and robust software that is less prone to vulnerabilities and data breaches. Customers today demand secure and reliable software, and this expectation can be achieved by implementing secure software development practices.
-
Cost Savings
Embracing secure software development practices early in the software development process can ultimately save organizations money. Addressing security issues in the early stages of development is less expensive than attempting to address a breach or vulnerability that occurs after deployment.
-
Regulatory Compliance
Regulatory requirements, such as the General Data Protection Regulation (GDPR) and the Payment Card Industry Data Security Standard (PCI DSS), require organizations to implement secure software development practices. By adhering to these standards, organizations can achieve regulatory compliance and avoid any violations or fines.
-
Competitive Advantage
By embracing secure software development, organizations can gain a competitive advantage. Offering customers reliable and secure software can differentiate an organization from its competitors and build trust among customers, which in turn can lead to increased market share.
How to Learn Secure Software Development
OffSec is a globally recognized and trusted provider of industry-leading cybersecurity training and certification programs. Among the comprehensive suite of learning paths that help learners adopt basic cybersecurity-adjacent concepts and cultivate the mindset necessary for a successful cybersecurity career, OffSec offers secure software development training for developers and security practitioners. Organizations worldwide turn to OffSec to enhance the skills and capabilities of their cybersecurity and developer teams in the following ways:
Build Foundational Secure Development Skills

Introduction to Secure Software Development
This learning path is designed for roles such as Security Software Engineer, Applications Engineer, Release Manager, Software Developer, or anyone committed to the defense or security of enterprise applications. Through a combination of content on language-agnostic secure coding principles, videos, and practical, real-world exercises, every development team will build skills applicable to a broad range of web technologies.
Start Your Secure Software Development Training
Build hands-on secure software development skills with OffSec training for individuals and teams.
Best value
Learn One
$2,749/year*
Includes one year of access to one 200 or 300-level course, the associated labs, and two exam attempts
Large teams
Learn Enterprise
Custom pricing
Unlimited OffSec Learning Library access with flexible terms and volume discounts available